Physical Infrastructure • On-Prem Compute • Private AI Systems
Direct Dispatch: (720) 694-1976 • [email protected] • Colorado Front Range • Nationwide
TismTek LLC
TismTek Infrastructure & Private AI Systems
Contact Engineering
The Partner In Your Corner

Technology moves fast.
Make sure the right team is watching your back.

Project managers and decision makers don't have time for finger-pointing, missed construction milestones, or high-pressure IT sales pitches. From the cable in the wall to the models in the room: we engineer structured cabling, fiber backbones, on-premises compute, and private AI systems with single-point accountability. Built right the first time, certified on paper, and owned completely by you.

100% Asset Ownership Zero recurring per-seat software retainers
In-House Field Techs Direct accountability, no unvetted subs
Certified Fluke Testing Pass/fail documentation on every drop
Rapid Front Range Response Dedicated local dispatch & national support
The Commercial Reality
Built for Project Managers Who Value Execution Over Excuses

When an infrastructure deployment fails or a network crashes, traditional IT companies sell another monthly retainer ticket. We see an engineering flaw that should have been solved at the physical and protocol layer from day one.

The Traditional IT & MSP Sales Trap
  • ×
    High-Pressure Retainers: Aggressive salespeople sell monthly per-seat licenses you don't need, trapping your operations in recurring subscription fees.
  • ×
    Subcontracting Roulette: They win your bid with slick presentations, then hand off the physical install to the lowest unvetted subcontractor on site.
  • ×
    Finger-Pointing on Downtime: When packets drop or switches fail, they blame your ISP or hardware vendor instead of taking ownership.
  • ×
    Rats' Nest Server Closets: Rushed, sloppy cabling without labeling or proper testing that causes intermittent outages down the road.
The TismTek Engineering Standard
  • ✓
    Complete Asset Ownership: You pay honest pricing for genuine engineering. When the job is done, you own 100% of your hardware and infrastructure.
  • ✓
    Direct In-House Craft: Experienced technicians on site who take pride in surgical cable combing, proper pathways, and tight milestone delivery.
  • ✓
    Single-Point Accountability: We own the physical and digital layer end-to-end. If there's an issue, we diagnose and solve the root cause.
  • ✓
    100% Certified Fluke Documentation: Every run is tested, mapped, and handed over in a clean as-built binder with zero shortcuts.
Engineering Capabilities
Physical Infrastructure, On-Prem Compute & Private AI

From the cable in the wall to the models in the room — one team accountable for every layer, built to standards you can audit and owned outright by you.

Structured Cabling

Commercial Cat6 & Cat6A plenum installations, pathway J-hooks, cable tray routing, patch panels, and point-to-point identification.

  • • 10GBASE-T Certified Testing
  • • ANSI/TIA-568-D Standards
  • • Combed Bundles & Clean Drops

Fiber Optic Infrastructure

Single-mode (OS2) and multi-mode (OM4/OM5) backbone cable pulls, precision fusion splicing, OTDR validation, and enclosure builds.

  • • Core Alignment Fusion Splicing
  • • Low-Loss LC/SC/MTP Connectors
  • • MDF-to-IDF Campus Links

Server Rack & MDF Buildouts

Design, assembly, power distribution, thermal airflow management, and structured patching for MDF/IDF telecom closets.

  • • 2-Post & 4-Post Equipment Racks
  • • Rack PDU & UPS Integration
  • • Color-Coded Patch Documentation

On-Premises Compute & GPU Systems

Racked Linux servers, workstations, and GPU systems sized for your workloads — virtualization, local storage, and 3-2-1 backups built into the design.

  • • GPU Builds for Inference & Training
  • • Commercial Linux Deployment
  • • Immutable Backup Pipelines

Private AI Systems

Run AI on your own hardware: local model serving, private assistants over your documents, and cost-governed model routing. Your data never leaves the building.

  • • On-Site Model Serving (vLLM, llama.cpp)
  • • Private Assistants Over Your Data
  • • Token Cost Governance & Routing

Zero-Trust Private Networking

End-to-end encrypted mesh networking, secure VLAN segmentation, hardware firewalls, and isolated subnets — the transport layer your AI and business systems live on.

  • • WireGuard Encrypted Topologies
  • • VLAN & IoT Segregation
  • • Zero Telemetry Leakage

Multi-Site Retail & Rollouts

Fast, disciplined rollouts for commercial facilities, POS register data drops, AP installs, and standardized build sheets across every location.

  • • Standardized Site Build Sheets
  • • Nationwide Coordination
  • • Per-Site Certification Packets

Data Protection & Disaster Recovery

3-2-1 backup architecture with encrypted off-site copies and documented restore drills — recovery you can verify, not a vendor promise.

  • • Immutable Snapshots
  • • Encrypted Off-Site Replicas
  • • Tested Restore Procedures

Root-Cause Systems Audits

In-depth inspection of existing physical pathways, network bottlenecks, and recurring failure points with actionable remediation plans.

  • • Physical Layer Signal Verification
  • • Network Topology Mapping
  • • Complete As-Built Documentation
Field Execution
Physical Layer Precision on Site

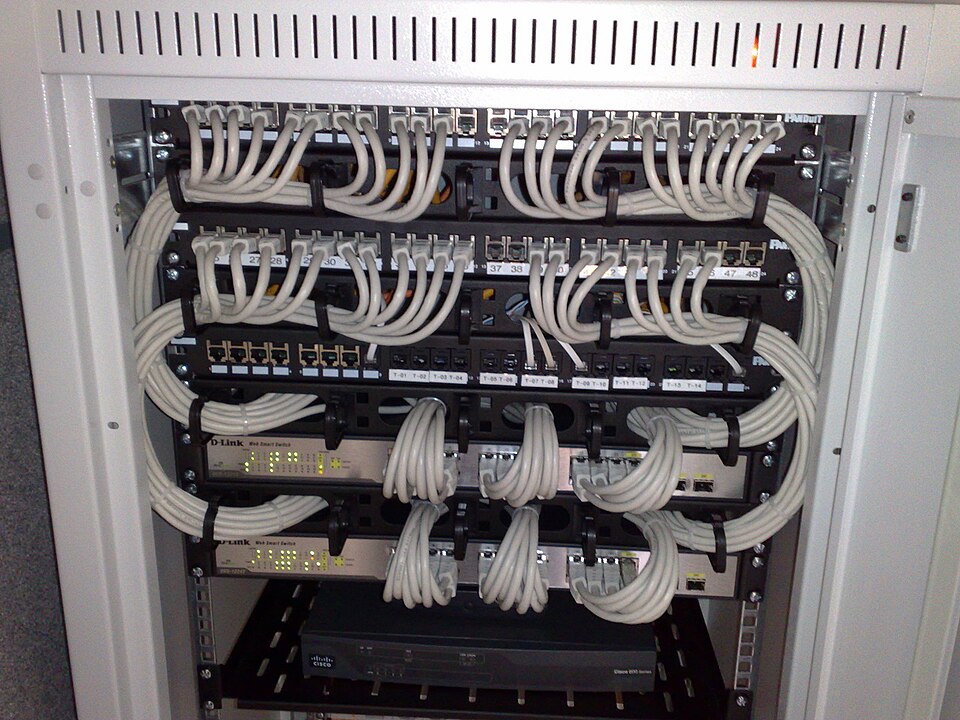
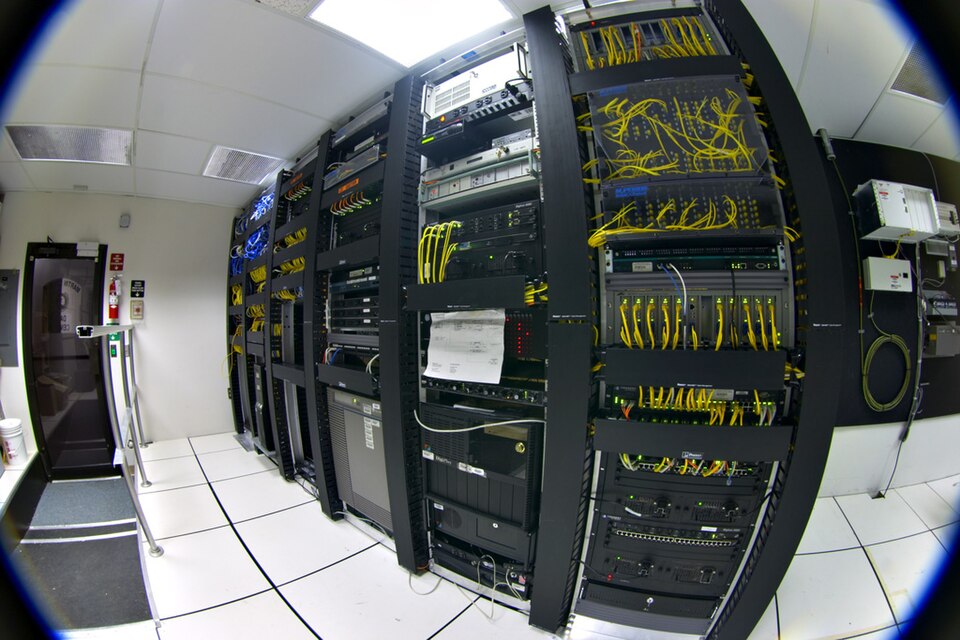
Structured cabling, telecom enclosures, and server room infrastructure deployed with surgical discipline and clean dressing.
Engineering Field Notes
Practical Guides & Industry Perspectives

Direct insights on structured cabling standards, physical layer testing, and sovereign infrastructure design.

Product Launch • New

TradeLeads Intel: Commercial Permit Leads, Published Weekly

Why an infrastructure contractor now publishes weekly permit-lead intelligence for subcontractors — coverage, limits, and a 3-per-territory cap.

Commercial Projects • Featured

How to Compare Commercial Low-Voltage Cabling Bids

A practical checklist for comparing cabling proposals by scope, pathways, testing, exclusions, and closeout documentation.

Commercial Infrastructure

Commercial Structured Cabling in Colorado: What to Specify Before Installation

The pathway, cable, rack, labeling, testing, and closeout decisions that make a commercial network serviceable.

Cabling Standards

Cat6 vs. Cat6A for Commercial Buildings: Which Should You Install?

How distance, wireless density, PoE loads, and future upgrades should shape the cable category decision.

Backbone Infrastructure

Fiber vs. Copper Network Backbones: A Practical Guide for Commercial Facilities

Where fiber, copper, MDFs, IDFs, and PoE each fit in a reliable commercial network backbone.

Plain English IT • Featured

Debunking Big Tech & MSP Buzzwords: Breaking the Vendor Lock-In Illusion

A friendly, plain-English guide decoding 'The Cloud', 'Zero Trust', and 'Single Pane of Glass' into everyday concepts anyone can understand.

Messaging Systems Analysis • New

Matrix and Synapse: Federated Encrypted Messaging in Practice

How homeserver ownership, federation, E2EE, Synapse releases, moderation, and reliability shape self-hosted messaging.

Self-Hosted AI Analysis • New

Open WebUI Self-Hosted AI: Upgrade Risk and Privacy Boundaries

A source-backed review of offline operation, Ollama, compatible APIs, RAG, tools, approvals, data boundaries, and safer upgrades.

Networking Analysis • New

Iroh Peer-to-Peer Networking: Keys, QUIC, NAT Traversal, and Limits

What Iroh 1.x actually delivers: key-addressed peers, direct paths, relay fallback, encrypted QUIC, multipath transports, self-hosting responsibilities, and limits.

Privacy Engineering Analysis • New

PySyft 0.10: Remote Data Workflows and Governance

How mock data, code review, approvals, privacy technologies, version changes, and output governance shape a remote data science workflow.

Systems Architecture

The Great Cloud Repatriation: Why Companies Are Bringing Workloads Back In-House

Why predictable enterprise workloads on rented public cloud instances cost 3x-5x more than owning your hardware outright.

Cabling Standards

Why WiFi 7 Doesn't Replace Good Copper: The Physics of Commercial Wireless

Why high-speed WiFi 7 access points still require certified multi-gigabit Cat6A backhaul to deliver real-world speeds.

Data Protection

The 3-2-1 Backup Strategy: Why Cloud Sync Is Not a Backup

Why folder syncing can amplify ransomware damage, and how to build an immutable snapshot pipeline for business continuity.

Physical Layer Power

Power Over Ethernet (PoE) in Modern Buildings: Beyond Basic Network Cameras

How 90W PoE++ powers commercial lighting, digital displays, and access control over structured low-voltage cables.

Testing & Compliance

What Fluke Certification Actually Tests (And Why Continuity Checks Aren't Enough)

Why a $15 continuity tester green light doesn't mean your Cat6A horizontal drops will pass 10GBASE-T under real network load.

Ground-Truth Reliability
Why Project Managers Trust TismTek on Site

When construction schedules are tight and general contractors demand clean execution, we deliver on time and under spec.

01 / Clean Physical Craftsmanship

We treat physical cabling as structural engineering. Proper bend radiuses, zero pinched conductors, hand-dressed hook-and-loop bundles, and total segregation from high-voltage lines.

02 / Transparent Milestone Communication

Project managers never have to guess our status. We provide clear daily logs, proactive coordination with other trades, and immediate escalation if site conditions change.

03 / Zero Ongoing Dependencies

We don't build systems designed to require monthly support contracts. Once tested, certified, and handed over, your team has complete documentation and operational autonomy.

Linux Workstation & Systems Engineering
Do you like Linux? We love Linux.

Finding an IT partner or MSP willing to properly deploy and support Linux workstations shouldn't be difficult.

Commercial Linux Desktop Deployment & Sovereign Infrastructure

Most traditional MSPs force every client onto proprietary operating systems simply because their per-seat ticketing and monitoring software demands it. If your team relies on Linux desktop workstations (Ubuntu, Debian, Fedora, Arch) for development, CAD, engineering, or privacy-first operations, we engineer and support your environment natively.

We handle structured provisioning, local storage and encrypted backups, WireGuard and mesh VPN topologies, and on-premises server stacks—delivering clean, dependable commercial IT without forced vendor lock-in or unnecessary licensing overhead.

Linux Workstation Deployment Anti-MSP Linux Support On-Premises Infrastructure Open Standards
Start The Conversation
Request a Project Bid or Infrastructure Consultation

Tell us about your upcoming facility buildout, commercial cabling scope, or network infrastructure goals.

Dispatch: (720) 694-1976
Territory: Colorado Front Range & Nationwide

PySyft Privacy-Preserving Data Science: Remote Workflows

Current Technical Notes
Release and operations notes

PySyft RDS 0.6: What the Package Split Changes

A practical, source-backed guide to the PySyft 0.10 package split, syft-rds 0.6, migration boundaries, and version pinning.

Read Article →

PySyft Permissions 0.1.15: Access Control Without Guesswork

How PySyft permissions 0.1.15 models read, create, write, and admin access, with a practical review and revocation checklist.

Read Article →

PySyft Migration 0.1.1: Versioned Objects and Compatibility

A practical explanation of PySyft migration 0.1.1, versioned objects, protocol schemas, and compatibility testing between peers.

Read Article →

PySyft Job 0.1.40: Review Execution and Protocol Compatibility

What PySyft job 0.1.40 is for, how its release artifacts protect compatibility, and what owners should test before execution.

Read Article →

PySyft Dataset 0.1.21: Mock and Private Assets

How PySyft dataset 0.1.21 fits mock data, private assets, permissions, and migration in a remote data workflow.

Read Article →

PySyft BG 0.3.12: Notifications and Auto-Approval

A practical review of PySyft BG 0.3.12 background services, notifications, strict auto-approval, and operational limits.

Read Article →

Kubo 0.43: Last Feature Release and Operator Checklist

What Kubo 0.43 adds, why its maintenance notice matters, and an operator checklist for IPFS upgrades and transition planning.

Read Article →

Kubo 0.42: Upgrade Notes for DHT and Storage Operators

A source-backed Kubo 0.42 operations guide covering DHT behavior, storage checks, browser retrieval, and upgrade evidence.

Read Article →

Headscale 0.29.3: Upgrade Notes for Tagged Nodes

What Headscale 0.29.3 fixes for tagged nodes, re-authentication, ephemeral peers, and capability checks.

Read Article →

Headscale 0.29.2: Registration and Policy Checks

A practical Headscale 0.29.2 guide to map generation, WebSocket registration, invalid names, and policy validation.

Read Article →

Iroh DNS 1.3.0: Release Scope and Upgrade Tests

What the Iroh DNS 1.3.0 tag tells operators, how it relates to Iroh 1.2, and which resolver tests matter.

Read Article →

Iroh 1.2: Relay Auth and DNS Changes to Test

A practical Iroh 1.2 guide to relay authorization signals, DNS fallback, mapped addresses, and dependency upgrades.

Read Article →

Open WebUI 0.11.3: Upgrade and Migration Failure Checks

What Open WebUI 0.11.3 changes, how migration failures now surface, and what self-hosted operators should verify.

Read Article →

Open WebUI 0.11.2: Operations Features Worth Testing

A practical Open WebUI 0.11.2 review covering previews, deployment overhead, request filters, and websocket behavior.

Read Article →

Open WebUI 0.11.1: How to Read the Release Safely

A source-backed Open WebUI 0.11.1 guide to release context, current configuration, integrations, and limits of self-hosting.

Read Article →

Kubo 0.43.1: What Shipped and What to Test

Kubo 0.43.1 changes gateway redirect headers and pins boxo 0.42.2. Here is what the release record says and the paths an operator should exercise first.

Read Article →

Kubo 0.40.1: The Windows Memory-Corruption Fix

Kubo 0.40.1 is a Windows-only patch. It downgrades the Go toolchain from 1.26 to 1.25 to fix a delayed daemon crash. Here is what the bug was and who should upgrade.

Read Article →

Kubo 0.41.0: Provider Records and Fast-Provide Controls

Kubo 0.41.0 gives the provider path real surface area: Provide.Strategy modifiers, fast-provide on pin, a fast-provide-dag flag, and a new ipfs cid inspect command.

Read Article →

Kubo 0.40.0: CID Profiles, Codec Controls, Delegated Routing

Kubo 0.40.0 adds UnixFS CID profiles, delegated routing for light clients, tighter gateway codec controls, and new diagnostics. Here is the operator-relevant surface.

Read Article →

iroh 1.0.0: Dialing Keys, Not IPs, and the Stable Release

iroh 1.0.0 is the stable release built around dialing peers by key rather than IP. Here is what it ships and what an operator should understand before running it.

Read Article →

iroh 1.0.1: Compatibility Fix and the DNS Fallback

iroh 1.0.1 is a focused patch over 1.0.0. It adds a backwards-compatibility item, caps log span levels, and introduces a DNS fallback for non-JNI environments.

Read Article →

iroh 1.0.2: Live Relay Rate-Limiting and Proto Hardening

iroh 1.0.2 is a small release whose headline is that the per-client relay rate limit can now be updated live, plus relay protocol and fairness hardening fixes.

Read Article →

iroh 1.1.0: Relay Metrics and Explicit Rate-Limit Signals

iroh 1.1.0 adds relay connection metrics and tells clients when they are being rate-limited. It also fixes relay reconnect behavior and breaks the CustomAddr serialization.

Read Article →

Headscale 0.29.0: SSH Check, Policy Tests, ACL Compatibility

Headscale 0.29.0 raises the minimum Tailscale client to 1.80.0 and adds SSH check actions, a beta policy-tests block, and improved Tailscale ACL compatibility.

Read Article →

Headscale 0.29.1: Preserving Users on null-Tagged Nodes

Headscale 0.29.1 is a one-line patch over 0.29.0: it stops nodes stored with tags='null' from losing their assigned user on upgrade. Here is the bug and who is affected.

Read Article →

Open WebUI 0.10.0: Sharing, Compaction, Memory, and Security Fixes

Open WebUI 0.10.0 adds folder sharing, context compaction, a reworked memory system, native hybrid search, an event system, and a security fix.

Read Article →

Open WebUI 0.9.6: Knowledge Base Sync and a Filesystem Tool

Open WebUI 0.9.6 makes knowledge bases practical at scale with the oikb sync tool, smart directory sync, nested folders, and a filesystem tool for models.

Read Article →

Open WebUI 0.10.1: The Shared-Folder Sign-Out Fix

Open WebUI 0.10.1 is a one-line patch: opening a read-only chat from a shared folder no longer signs the user out. Here is the bug and how it matters on a shared instance.

Read Article →

Open WebUI 0.10.2: Streamed Reasoning and Security Fixes

Open WebUI 0.10.2 adds streamed reasoning display, folder uploads, a memory context toggle, and a security advisory with logout and search-filter fixes.

Read Article →

Open WebUI 0.9.5: SSRF Protection and Permission Enforcement

Open WebUI 0.9.5 adds redirect-based SSRF protection, an iframe content-security policy, and closes a set of permission-enforcement gaps on a shared instance.

Read Article →